
Fixes that merge themselves
Decide how far a security fix goes before anyone is asked, from a note on the finding to a verified merge into main, set per kind of finding.
Knowing about a vulnerability is rarely the hard part. The fix waits for someone to plan it, build it and press merge, behind everything else the team has on.
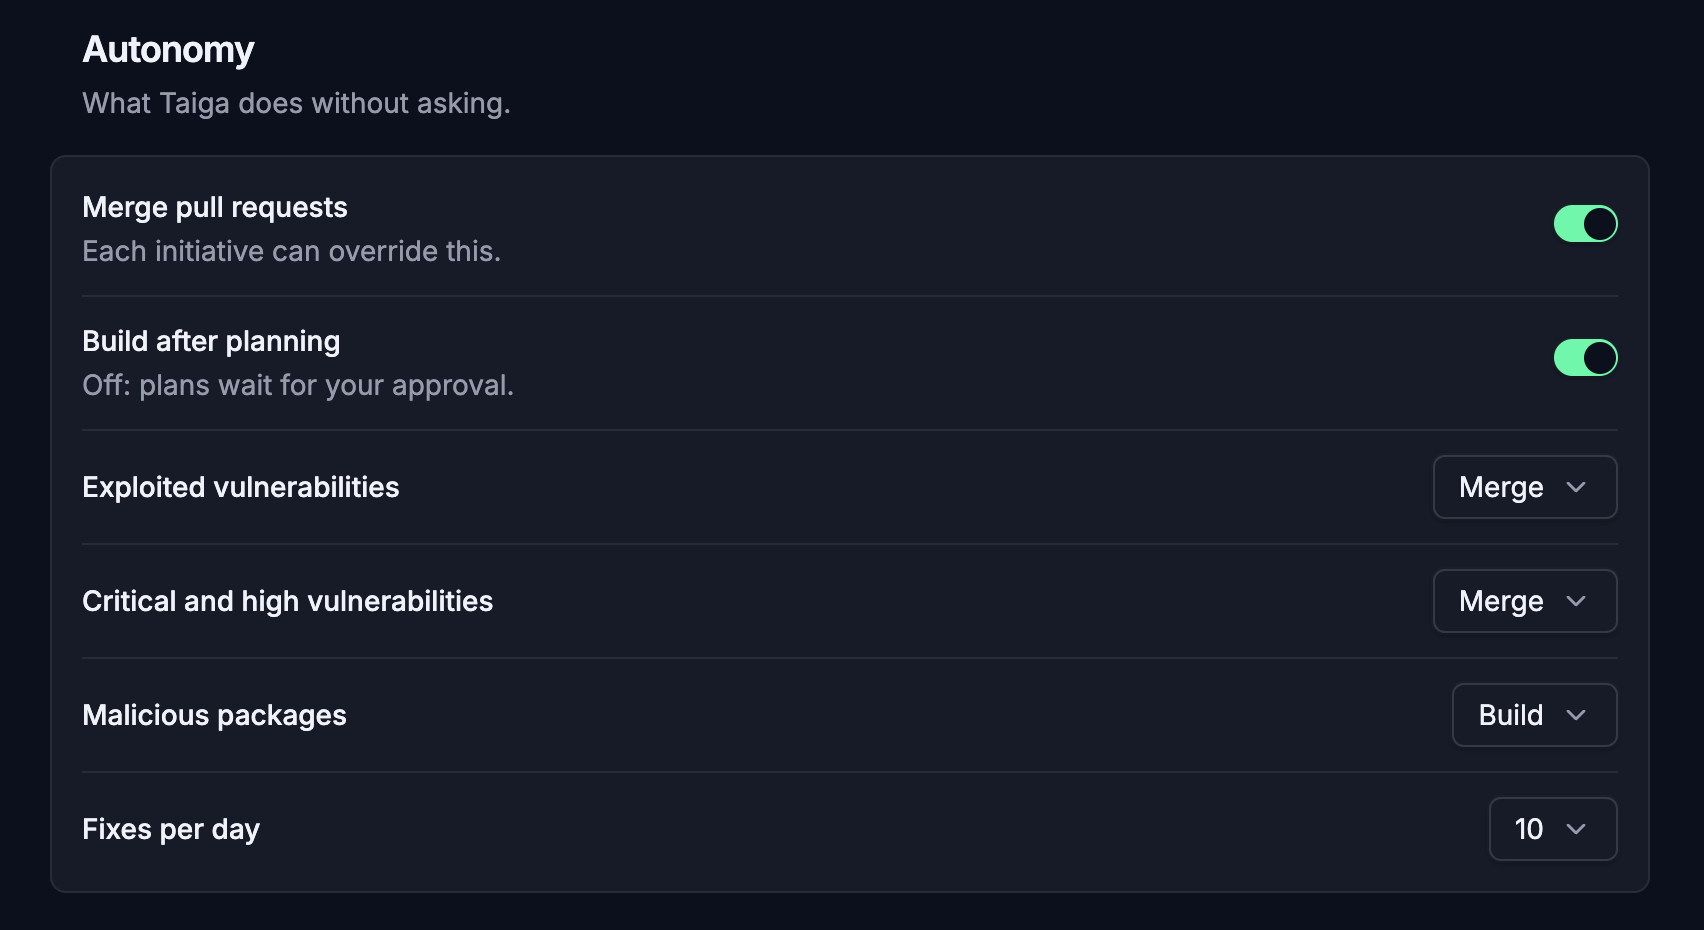
How far a fix goes on its own is now a setting per kind of finding: exploited vulnerabilities, critical and high ones, and malicious packages. Notify leaves the decision with you, Plan and Build put a plan or a pull request in front of you, and Merge puts the fix in main. Nothing merges until an independent re-scan confirms the vulnerability is gone. Exploited findings go to the front of the queue, and a daily limit keeps the pace yours.
Sweeps also look further than the lockfile: the runtime a service ships on, starting with Node.js, is checked against its own security releases.
Every fix raised, and every one held back, is in the audit log with the reason. Set exploited vulnerabilities to Merge, and the fix is in main before standup.
Security debt stops waiting for a free afternoon.
Every change, dated the day it shipped.
Dated the day they shipped, newest first.